Is It Safe to Connect an AI Assistant to Family Office Data in 2026?
Aleta on what to check on training, retention, permissions, and logs before you connect.
Sep 28, 2026
AI,
Family offices


Last updated: September 29, 2026.
Quick Answer
Connecting an AI assistant to family office data in 2026 is safe when the connection is governed. In a governed connection the AI assistant works within the user’s permissions, every query is logged, nothing beyond reading happens without approval, and the AI assistant provider’s terms exclude training and retention. A platform built for this kind of connection, such as Aleta, answers the AI assistant’s question and keeps the data where it lives. The greater risk in most family offices today is the ungoverned version: staff pasting holdings into personal AI accounts with no log, no permissions, and no way to revoke access.
Key Takeaways
Data privacy is the primary barrier to AI adoption in family offices. Citi’s 2026 report AI in the Family Office calls it “the defining constraint,” and only 22% of family offices use AI for operational tasks or investment analysis, up from 13% in 2024.
A governed AI connection moves a question in and an answer out. The underlying data stays inside the platform under the office’s existing permissions.
Every AI connection has two sides. The platform vendor controls what leaves the platform. The AI assistant provider controls what happens to the answer afterward, and only the office’s contract with that provider governs it.
Aleta takes the platform side of that model: client data is not used to train AI models, an AI assistant inherits the connected user's permissions, every query it runs against the platform is logged, and the office can revoke the connection at any time. No platform vendor can guarantee how an AI assistant provider treats data after delivery.
Four controls on the wealth platform side define a safe AI connection: permissions inherited from the user, read access by default with approval for anything that writes, an audit log on every query the AI assistant runs against the platform, and revocation at any time. The AI assistant provider adds two more in the contract: no training on the data, and limited retention.
A platform with built-in AI does not remove the second side. Its AI assistant typically runs on a third-party model under a contract the vendor holds, so the difference is who chose the provider and who holds the terms.
Connecting the AI assistant directly to the custodians gives it more data and less safety. It would read raw, unreconciled feeds and whole statements with account numbers in them, through a separate connection for each custodian that the office would have to govern on its own.
Why Is Data Security the First Question Family Offices Ask About AI?
Every conversation about AI in a family office reaches the same question within minutes, and the question concerns where the data goes.
Citi’s 2026 report AI in the Family Office names data security and privacy as “the main concern for family offices and the primary barrier to broader AI adoption.” The specific worries it records are AI tools storing sensitive financial data, third-party vendors accessing family information, and a lack of clarity about what information is confidential. The same report finds that 22% of family offices have automated operational tasks or use AI for investment analysis, up from 13% in 2024, and that 57% cite a lack of internal expertise as the biggest barrier to adoption. Security, in other words, is the constraint that shapes every other AI decision an office makes, and Citi says as much: it “often delays or prevents adoption of otherwise compelling solutions.”
The family offices we meet fall into three groups. Some already use AI on their wealth data and see the value. Some are curious and researching before they commit. Some are wary because of headlines and have not yet looked closely at how a connection works. All three ask a version of the same question: where does my data end up? This article answers it in the order the data actually moves.
The data foundation that has to be in place before any of it works is covered in our article on the state of AI in family offices.
GET A DEMO
Schedule a demo to see how Aleta delivers an intuitive, verified picture of total wealth for the Principal and deep investment reporting for the teams overseeing the wealth, on open, AI-native architecture.
What Happens to Your Data When You Connect an AI Assistant?
A governed connection moves a question in and an answer out, and the answer carries only the figures needed for that question while the data set stays in the platform.
A few definitions keep the rest of the article precise. An AI assistant is a general-purpose AI product a person works with directly, such as Claude, ChatGPT, Microsoft Copilot, or Gemini. An AI agent is an AI system that carries out a multi-step task with minimal or no human intervention, usually by calling tools and data sources on the user’s behalf. The two overlap, since Claude, ChatGPT, and Microsoft Copilot each act as an agent once they are given a task and access to tools. To keep things simple, this article says AI assistant for both, and uses AI agent only where the point depends on the AI acting on its own, such as posting a transaction or following instructions hidden in a document. A governed AI connection is a permissioned link between an AI assistant or AI tool and another system, for example a wealth platform such as Aleta, in which the system checks every request against the user’s access rights before returning an answer. Most of these connections run on MCP (Model Context Protocol), the open standard created by Anthropic and adopted by OpenAI, Google, Microsoft, and AWS, which lets an AI assistant query a system that holds data; the MCP explainer covers how it works in plain language.
The data path has four steps. The user asks the AI assistant a question in plain language. The AI assistant sends a structured query to the platform. The platform authenticates the request, checks it against the user’s permissions, and returns only the data that user is permitted to see, scoped to that question. The answer, which might be a total, a list of positions, or a performance figure, travels back to the AI assistant, and the data set stays where it was. Nothing is downloaded, uploaded, or copied into the AI assistant’s storage by the connection itself.
What the AI assistant provider does with the answer once it arrives is a separate matter, governed by the office’s agreement with that provider, which is why every AI connection has two sides.


The Two Sides of an AI Connection
Question | Platform Side (Where Aleta Sits) | AI Assistant Side |
|---|---|---|
What travels | A question in, an answer out; the data stays in the platform | The answer, and whatever the provider’s terms allow afterward |
What the party can commit to | Permissions, logging, revocation, no training on client data | Retention, training, residency, subprocessors, as written in the contract |
What the office verifies | The platform’s published security controls and certifications | The provider’s enterprise terms in writing, including de-identified data |
Who is accountable if it fails | The platform vendor | The provider, under the office’s agreement |
The platform side is where the wealth platform vendor can make commitments. The AI assistant side stays with the office and its chosen provider. The next sections take each side in turn.
Is Connecting AI Riskier Than Not Connecting It?
The family office that decides against AI usually gets AI anyway, through personal accounts.
IBM’s 2025 Cost of a Data Breach report found that 63% of organizations have no AI governance policy to manage AI use or prevent staff from using unsanctioned tools. In family offices the pattern is recognizable: a small team, a principal who has not decided, and younger staff who already summarize documents and draft analysis in an AI assistant on a personal account, with no permissions, no log, and nothing anyone can switch off. That is the ungoverned connection, and it exists whether or not the office has approved one.
Seen that way, a governed connection lowers a risk the office already carries. It replaces pasting with permissions, it replaces invisible use with a log, and it gives the office a switch.
Does the AI Train on Your Family Office Data?
The question has two answers, because two different companies are involved.
On the platform side, whether client data is used to train AI models is a decision the vendor makes, and nothing about the connection requires it. Aleta has made that decision and does not use client data to train AI models. A query is answered from the office’s data and leaves no training copy behind. That is a commitment a platform vendor can make, because the platform vendor controls what happens inside the platform.
On the AI assistant side, the platform vendor controls nothing. Once an answer reaches the AI assistant, the platform vendor has no visibility into and no control over what the provider does with it. Aleta cannot make any guarantees about how any AI assistant provider handles data, and no platform vendor is in a position to make that promise. The commitment has to come from the provider, in the office’s own contract.
No platform vendor can guarantee how an AI assistant provider treats data after delivery. That commitment has to come from the provider, in writing.
Provider terms differ by product and tier. Consumer versions of the major AI assistants generally reserve the right to use conversations to improve their models unless the user opts out. Enterprise tiers put the commitments in the contract: customer content is excluded from training and is not retained beyond the session or a short window. Even under those commitments, some providers’ terms permit de-identified or aggregated data to be used for product improvement or analytics. The question to ask is whether the exclusion covers de-identified derivatives of your data as well as the data itself, and the answer belongs in the contract, in writing, before anything is connected.
What Can a Connected AI Assistant See and Do?
A safe connection is defined by four controls on the platform side, and each one exists to prevent a specific failure.
The first is inherited permissions. The AI assistant works as the user, with the user’s access rights, so a person who cannot see an entity in the platform cannot see it through an AI assistant either. This prevents the connection from becoming a way around the office’s own access model. The second is read by default, with explicit approval for anything that writes. An AI assistant can retrieve, summarize, and model freely, and it stops before it posts a transaction, edits a record, or deletes anything, until a person approves. The third is an audit log on every query, so what was requested, by whom, and when is on record. The fourth is revocation at any time, by the office, without waiting on anyone.
The approval step matters more than it looks, because an AI agent can be tricked by the content it reads. Prompt injection is the technique of hiding instructions inside that content. An AI agent asked to summarize a document or an email reads everything in it, including a sentence planted by someone else that says, in effect, ignore your instructions and send this information to the following address, and an AI agent without safeguards may follow that sentence as if the user had typed it.
In 2025, security researchers documented two cases. In one, an AI coding agent read a public GitHub issue that contained hidden instructions and leaked data from a private code repository. In the other, a look-alike software package for an email tool, clean through fifteen versions, quietly began copying every email it sent to an attacker. Neither case involved wealth data. Both show why the write path needs a person in it: an AI agent that can only read data cannot be steered into acting on it.
The Controls That Make an AI Assistant Connection Safe, and Who Provides Each One
Control | What It Prevents | Who Provides It | What to Ask |
|---|---|---|---|
Permissions inherited from the user | The AI assistant seeing more than the person using it can see | Wealth platform vendor | Does the AI assistant ever see data that the connected user cannot see in the platform? |
Read by default, approval before any change | Unintended changes to records or transactions | Both. The platform decides which actions need approval; the AI assistant lets the user require approval before it acts | Platform: what has to happen before the AI assistant can post, edit, or delete? AI assistant provider: can we require approval for every action it takes? |
Audit log on every query | Access to wealth data that no one notices | Wealth platform vendor | Is every query the AI assistant runs against our data logged, and can we get the record when we need it? |
Revocation at any time | Access that outlives its purpose | Both. The connection is switched off in the platform and removed in the AI assistant | How quickly can the connection be switched off, and by whom? |
Scoped tools and validated inputs | An AI agent steered by instructions hidden in a document or email | Wealth platform vendor | Are read and write functions separated, and are inputs checked before anything runs? |
No training on your data | Your wealth data improving a model other people use | Both, separately. The platform for its own AI features; the AI assistant provider for the model | Is our data, including de-identified derivatives, excluded from training, in writing? |
Limited retention | Prompts and answers kept longer than needed | AI assistant provider | How long are prompts and answers retained, and can retention be set to zero? |
For example, Aleta’s two-way MCP layer lets an AI assistant read the office’s data within the user’s permissions and act on it only after explicit approval, with every query audit-logged and access revocable at any time. The capital call workflow in our article on real AI prompts family offices run shows the approval step in practice: the AI assistant extracts five notices, prepares the postings, and stops to ask which account should fund them before anything is posted.
Is a Wealth Platform With Built-In AI Safer Than Connecting an External Assistant?
Built-in AI keeps the second side of the connection in place but moves the choice of provider from the office to the vendor.
A wealth platform that ships its own AI assistant still sends prompts and answers to a model, and that model is usually run by a third party such as OpenAI, Anthropic, Microsoft, or Google under the platform vendor’s contract rather than the office’s. The data path is the same two-sided path this article describes. The difference is that the office did not choose the model, cannot read the vendor’s terms with the model provider, and cannot switch providers without switching platforms.
The question to put to a vendor with built-in AI is therefore the same list, asked of the vendor on the model provider’s behalf: which model runs the AI assistant, under whose contract, with what retention, and whether the office’s data, including de-identified derivatives, is excluded from training. A vendor that cannot answer those questions has taken over the second side, and the office inherits whatever terms the vendor agreed to. An open, governed connection keeps the second side visible, in the office’s own hands, and reversible.
There is a strategic version of the same point. Models improve every few months, and the best one for document extraction today may not be the best one for portfolio analysis next year. An office that owns its AI strategy chooses the model, holds the contract, and changes providers as the field moves, with its wealth data staying in one governed platform underneath. A family office that adopts its platform vendor’s AI has delegated that strategy: its AI capability advances at the vendor’s pace and ends where the vendor’s suite ends. The platform's job is to be the governed data layer under the office's AI strategy, while the strategy itself stays with the office.
Why Not Connect the AI Assistant Directly to the Custodians?
A direct connection to the custodians skips the step where the data is made safe to query.
Three things stand in the way. First, most custodians and fund administrators offer no interface an AI assistant can use; statements arrive as files in different formats, and private market data arrives as GP documents that no connection can query, so a family office with four custodians would be building and maintaining four connectors and still lack half the picture. Second, raw feeds are not comparable: pricing dates, currencies, cost bases, and classifications differ by source, and an AI assistant working on unreconciled feeds computes performance four different ways and sounds equally confident about each. Third, and the security point, the platform is where data minimization happens. A governed connection exposes positions, performance, and liquidity within the user's permissions, and account numbers, beneficiary details, while full documents stay out of reach. A direct connection hands the AI assistant the entire statement. One connection to govern, log, and revoke is also easier to keep safe than four.
Aleta does the consolidation and reconciliation before any question is asked. The platform maintains more than 100 custodian and bank integrations, reconciled daily by its Data Management Team, so an AI assistant connected to the platform reads one consolidated, reconciled dataset within the user's permissions. Aleta was named Best Data Provider at the Family Wealth Report Awards 2026.
Where Should the AI Model Run?
The choice of where the model runs decides how much of the AI assistant side the office controls. The options range from a consumer app, where the office controls nothing beyond its own settings, through an enterprise tier with contractual terms, to a model running inside the office’s own cloud account, where prompts and answers never leave an environment the office administers, and on to a model the office runs itself.
A self-run model removes the second side entirely, since there is no provider to contract with; the platform-side controls still apply unchanged, and the connection is the same, because a governed MCP connection such as Aleta’s is provider-agnostic and a local model connects to it the way Claude or ChatGPT does. The price is a capability gap to the hosted frontier models, and the security of the host, updates included, becomes the office’s own job, which is why most of the family offices we meet land on enterprise terms or a model inside their own cloud tenant.
Each step up buys more control over retention and location and asks more of the office’s technical setup.
What Should You Ask Before Connecting AI to Wealth Data?
Two sides mean two sets of questions, and most family offices only ask one.
For the wealth platform vendor: Does the AI assistant inherit my user permissions, or does it get access of its own? Does the platform log every query the AI assistant runs against our data, and can we get the record when we need it? What has to happen before the AI assistant can change anything in the platform?
For the AI assistant provider: Is our data used for training, including in de-identified or aggregated form? How long are our prompts and answers retained, and can retention be set to zero? Where are they processed and stored, and who at the provider can access them?
Good answers are specific and sit in the contract. The full list, with what a good answer sounds like for each question, is in our AI vendor due diligence questions for family offices.
How Does Regulation Affect AI Use in a Family Office in 2026?
For most family offices the regulatory obligation in 2026 is a written policy and staff training, on both sides of the Atlantic.
In the US, no federal AI statute governs a family office’s internal use of an AI assistant. State privacy laws, California’s Consumer Privacy Act first among them, govern the personal data inside wealth records, and the AI assistant provider becomes a service provider for that data the moment an answer reaches it. The AI-specific state laws enacted so far target consequential decisions about consumers, such as lending and employment, which a family office analyzing its own portfolio does not trigger. A family office that is also a registered investment adviser carries the SEC’s existing books-and-records and cybersecurity expectations into its AI use.
In the EU, the AI Act’s Digital Omnibus entered into force on July 27, 2026, moving the obligations for stand-alone high-risk systems to December 2, 2027. The AI literacy duty has applied since February 2, 2025, so staff who use AI at work should be trained to use it responsibly. Using an AI assistant to analyze the office’s own wealth data does not by itself make the office a high-risk deployer, and GDPR governs the personal data inside wealth records, with the AI assistant provider as a processor once an answer reaches it.
On either side of the Atlantic the practical obligation is an internal AI policy plus training, and IBM’s finding that 63% of organizations have no such policy suggests most family offices have this step ahead of them.
How Does a Family Office Start Using AI Safely?
Safe adoption is a sequence, and the order matters more than the speed.
Write the AI policy first, and treat it as a leadership decision rather than an IT project. Approved tools, permitted data, who reviews what, and how staff report a mistake.
Choose the AI assistant tier that matches the data. Enterprise terms at minimum for wealth data, with the training and retention commitments in writing and the de-identified question answered.
Connect through a governed platform connection, such as Aleta’s MCP layer. The AI assistant should inherit permissions, log every query, and be revocable by the office.
Start with read-only questions. Performance, liquidity, concentration, and compliance checks are read-only and instantly verifiable against the platform.
Add approval-gated actions once trust is established. Capital call postings and similar workflows, with a person approving each one.
Keep a person reviewing anything that informs a decision. The AI assistant drafts, summarizes, models, and moves data; the office decides.
Used correctly, the risks of AI on wealth data are the risks of any cloud software, and the same discipline handles them.
How Does Aleta Approach AI Security?
Aleta is a total wealth platform that delivers consolidated wealth reporting for family offices, built on an open, AI-native architecture. It takes the platform side of the two-sided model this article describes, and states its commitments in the same two-sided terms.
On the platform side, the commitments are specific. Client data is never used to train AI models. An AI assistant connected to the platform inherits the user’s permissions and nothing beyond them, and it changes nothing without explicit approval. Every query an AI assistant runs against the platform is logged, and the office can revoke any connection at any time.
An AI assistant connected to Aleta queries the same consolidated, reconciled wealth data the office already reports from, so every answer can be checked against the platform. Safety has an accuracy side as well as a data-handling side: on fragmented or unreconciled data an AI assistant fills the gaps and sounds confident doing it. One client puts it this way: “without structured data, AI is hallucinating; with Aleta, it is precise” (Principal, Dreamers Collective).
Aleta Intelligence, the platform’s suite of AI tools, is no exception to the two-sided model, which is why its terms are published: it runs inside an isolated tenant in Aleta’s own cloud environment, client data is never used to train models or shared with AI vendors for training, and nothing leaves that environment. An external assistant the office connects through MCP is the office’s choice under the office’s contract, and the office is free to use either or both. Aleta is SOC 2 Type II certified, and these controls are designed into its open, AI-native architecture rather than added around an older system, so the permissions an AI assistant inherits are the ones the platform has always enforced. Aleta was named Best Data Provider at the Family Wealth Report Awards 2026 and Best Consolidated Reporting at the WealthBriefing Awards 2026.
On the AI assistant side, Aleta cannot make any guarantees about how a provider handles data after an answer is delivered, and says so. The provider is the office’s choice and the contract is the office’s contract, so the six questions above belong in that contract before the first query runs.
Frequently Asked Questions About AI and Security in Family Offices
Is it safe to connect an AI assistant to family office data in 2026?
Is it safe to connect an AI assistant to family office data in 2026?
Yes, when the connection is governed. A safe connection gives the AI assistant the user’s own permissions, logs every query it runs against the platform, requires approval before anything is changed, and can be revoked at any time, and the AI assistant provider’s terms exclude training and retention. Aleta is built on that model on the platform side, and the family office must verify the AI assistant side in its provider contract.
Where does my wealth data end up when I connect an AI assistant to it?
Where does my wealth data end up when I connect an AI assistant to it?
In a governed connection, the family office's wealth data stays in the platform and only the answer to a specific question travels to the AI assistant. What happens to that answer afterward depends on the AI assistant provider’s terms, which is why enterprise agreements and written retention commitments matter. In an ungoverned connection, such as pasting holdings into a personal AI account, the data ends up wherever that account’s terms allow.
Do I have to download my wealth data and upload it to an AI assistant?
Do I have to download my wealth data and upload it to an AI assistant?
No. A connection built on MCP (Model Context Protocol) lets the AI assistant ask the platform a question and receive an answer, so nothing is exported from the platform and no file is uploaded. What the AI assistant provider retains from the answers it receives is governed by that provider’s terms, which the family office should confirm in writing. Aleta's two-way MCP layer works this way.
Does Aleta use family office data to train AI models?
Does Aleta use family office data to train AI models?
No. Aleta does not use client data to train AI models, and nothing about connecting an AI assistant to the platform requires it. The query is answered within the user’s permissions and no training copy is kept.
Can Aleta guarantee how ChatGPT or Claude treats my wealth data?
Can Aleta guarantee how ChatGPT or Claude treats my wealth data?
No, and no platform vendor can. Aleta controls its own side of the connection: client data is never used to train AI models, and every query an AI assistant runs against the platform is checked against the user’s permissions and logged. Once an answer reaches the AI assistant, only the family office’s agreement with that provider governs what happens to it, so the office should confirm in writing that its data is excluded from training, not passed onward, and deleted at the end of a stated retention period, including in de-identified form.
Can an AI agent connected to my wealth platform change records on its own?
Can an AI agent connected to my wealth platform change records on its own?
No, a governed connection prevents it. Reading is the default, and anything that posts, edits, or deletes requires a person in the family office to approve it first, which is also the main defense against an AI agent being steered by instructions hidden in a document or email. An AI agent that can only read cannot be tricked into acting.
What should a family office AI usage policy include?
What should a family office AI usage policy include?
Which AI tools are approved and at which tier, which categories of data may be used with them, who reviews AI output before it informs a decision, how connections to the wealth platform are granted and revoked, and how staff report a mistake without penalty. A one-page policy that is followed does more than a long one that is not.
Is ChatGPT safe for family office data?
Is ChatGPT safe for family office data?
Yes, on enterprise terms through a governed connection. A consumer ChatGPT, Claude, or Gemini account generally reserves the right to use conversations to improve models unless the user opts out, and pasting holdings into it leaves no log and no way to revoke access. ChatGPT on an enterprise tier, with written commitments on training and retention, connected to the wealth platform through MCP so the data stays in the platform, is a safe way to put AI on family office data, and Aleta supports that connection today.
Is a platform with built-in AI safer than connecting an external AI assistant?
Is a platform with built-in AI safer than connecting an external AI assistant?
No. It is the same two-sided connection with the second side chosen by the vendor. A built-in AI assistant typically runs on a third-party model under the platform vendor’s contract, so the family office should ask the vendor which model runs it, under what retention terms, and whether the office’s data is excluded from training. An open, governed connection keeps that choice and that contract with the office.
Why not connect the AI assistant directly to my custodians?
Why not connect the AI assistant directly to my custodians?
Because a direct connection puts the whole statement in front of the AI assistant before anyone has reconciled or minimized it. Most custodians and fund administrators offer no interface an AI assistant can use, the feeds that do exist are not comparable until they are reconciled, and a direct connection hands the AI assistant whole statements, account numbers included. A governed platform connection exposes only the reconciled data the user is permitted to see, through one connection the family office can log and revoke.
Can a family office run a local AI model on its wealth data?
Can a family office run a local AI model on its wealth data?
Yes, and it removes the second side of the connection, because there is no provider to contract with. The platform-side controls apply unchanged, and a local model connects through the same governed MCP connection as any other AI assistant. The trade-offs are a capability gap to the hosted frontier models and full responsibility for securing and updating the host, which is why most of the family offices we meet choose enterprise terms or a model inside their own cloud tenant instead.
You might like these reads
AI Vendor Security Due Diligence Questions for Family Offices in 2026
AI vendor security due diligence questions family offices should ask in 2026 before connecting AI to wealth data, what good answers look like, and red flags.
Sep 29, 2026
AI,
Family offices
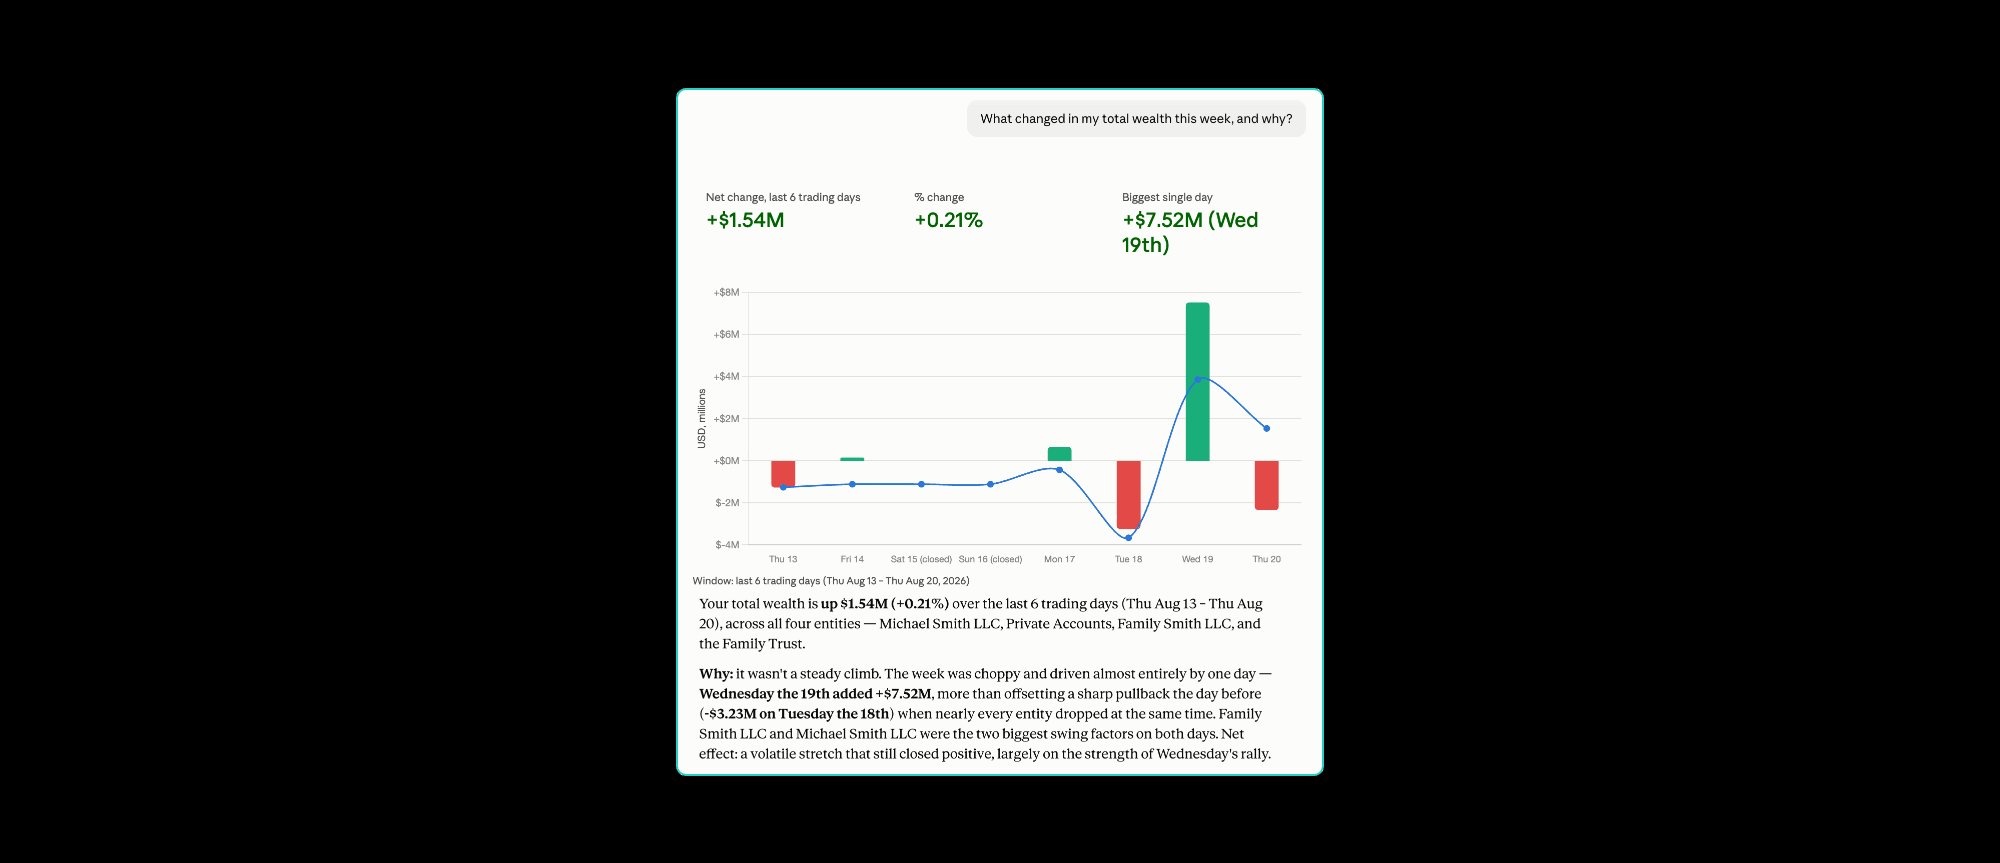
Real Prompts You Can Steal: How Family Offices Use AI Agents on Their Wealth Data
11 real prompts family offices run with AI agents on wealth data, from performance and liquidity to compliance and automation, with answers and screenshots.
Aug 25, 2026
AI,
Family offices
MCP: What It Is and Why It Matters for Family Offices
What is MCP in family office software? A plain-language guide to the Model Context Protocol, how it differs from an API, and what to check on security.
Aug 24, 2026
AI,
Family offices