AI Vendor Security Due Diligence Questions for Family Offices in 2026
AI vendor security due diligence questions family offices should ask in 2026 before connecting AI to wealth data, what good answers look like, and red flags.
Sep 29, 2026
AI,
Family offices


Last updated: September 29, 2026.
Quick Answer
AI vendor security due diligence for a family office goes to two vendors: the AI assistant provider whose model reads the office’s data, and the software vendor, such as the wealth platform, that connects to it. Five questions decide most evaluations: training on the data, including in de-identified form; retention and whether it can be set to zero; where the data is processed and who can see it; whether the AI assistant inherits the user’s permissions and needs approval before acting; and what happens to the data at contract end. Good answers are specific and sit in the contract, and a platform vendor such as Aleta publishes its answers while the office verifies the AI assistant provider separately. Capability, fit, and price are a separate evaluation that this article does not cover.
Key Takeaways
Third-party risk featured in 40% of cyberattacks on family businesses in the past two years, while 32% rely on vendor governance as a control, according to Deloitte’s 2026 family business cybersecurity report.
77% of family offices expect their use of third parties to increase over the next three years, and Ocorian’s 2026 Global Family Office Report notes that when services are externalized, data moves with them.
Every AI assistant provider a family office connects is a new subprocessor of its wealth data, with its own retention and training terms.
A no-training commitment that excludes only identifiable data still allows the vendor to learn from the office’s data in aggregate. The question that separates a real commitment from a nominal one is whether de-identified derivatives are excluded as well.
AI vendor due diligence repeats whenever the vendor changes its model, its subprocessors, or its terms, and at least once a year regardless.
A wealth platform vendor can publish its platform-side answers, and Aleta does: no training on client data, permissions inherited from the user, approval before any change, every query logged, and revocation by the office. The AI assistant provider's answers come only from its enterprise contract.
Why Does AI Vendor Security Due Diligence Matter for Family Offices?
Vendor governance is one of the least used security controls among family businesses, relied on by 32% according to Deloitte’s 2026 report, and AI tools are the newest vendors on the list.
Deloitte’s 2026 family business cybersecurity report found that 74% of family businesses experienced at least one cyberattack in the past two years, that third-party risk featured in 40% of those attacks, and that only 32% rely on vendor governance as a security control. Ocorian’s 2026 Global Family Office Report adds the direction of travel: 77% of family offices expect their use of third parties to increase over the next three years, 19% name cybersecurity concerns as one of the reasons, and the report observes that “when services are externalised, data moves with them.” Citi’s 2026 report AI in the Family Office lists third-party vendors accessing family information as one of the three specific worries behind the data privacy concern that it calls the primary barrier to AI adoption.
An AI assistant is a third party of exactly this kind. The moment an answer about the office’s holdings reaches it, the provider holds a piece of the office’s wealth data under terms the office may never have read. The connection can sit outside the office’s usual procurement process, since the tool is a monthly subscription and the person connecting it may be an analyst, so the vendor review that would meet a new custodian does not always meet a new AI tool. The questions below give that connection the same scrutiny, in a form a family office can complete in an afternoon.
GET A DEMO
Schedule a demo to see how Aleta delivers an intuitive, verified picture of total wealth for the Principal and deep investment reporting for the teams overseeing the wealth, on open, AI-native architecture.
Which AI Vendors Need Due Diligence?
Three kinds of vendor touch the office’s data with AI, and each one answers a different subset of the questions.
A few definitions first. AI vendor security due diligence is the process of verifying, before and during a contract, how a vendor’s AI handles the office’s data, who can access it, and what the office can enforce if the vendor’s answers turn out to be wrong. A subprocessor is any company that processes the office’s data on behalf of a vendor the office has contracted with, so an AI assistant provider used by a software vendor is the office’s subprocessor even when the office never signed anything with it. An enterprise tier is the version of an AI product sold to organizations under negotiated terms, as distinct from the consumer version sold to individuals under standard terms. Zero data retention is a contractual arrangement in which the AI provider does not store prompts or answers after the response is delivered. A data processing agreement, or DPA, is the contract clause or addendum that sets out what a vendor may do with personal data on the office’s behalf.
Table 1. The three kinds of AI vendor a family office evaluates
Vendor Type | Examples | What the Family Office's Data Does There | Who Answers the Questions |
|---|---|---|---|
AI assistant provider | Anthropic (Claude), OpenAI (ChatGPT), Microsoft (Copilot), Google (Gemini) | Prompts and answers pass through the provider’s model and are retained under the provider’s terms | The provider, in its enterprise contract |
Software vendor adding AI to a product the office already uses | A wealth platform, a general ledger, a document tool | The vendor’s own AI features process the data inside the product, and any connection to an outside AI assistant passes answers to that provider | The software vendor for its side; the AI assistant provider for its side |
Service provider using AI on the office’s behalf | An outsourced administrator, accountant, or law firm using AI tools internally | The office’s documents and figures enter whichever AI tools the provider has chosen | The service provider, which should disclose its own AI vendors |
The second row is where most wealth data sits. A platform such as Aleta exposes the office’s data through an open API with an MCP (Model Context Protocol) layer on top for AI agents, so the platform answers for what an AI assistant can see and do inside the platform, and the AI assistant provider answers for what happens to the answer afterward. Our article on whether it is safe to connect an AI assistant to family office data explains that two-sided model in full, and our article on the state of AI in family offices covers the data foundation underneath it. This article assumes both and moves to the questions.
What Data Handling Questions Should You Ask an AI Vendor?
Six questions cover how an AI vendor treats the data itself, and the first one carries a second half that decides whether the answer means anything.
Table 2. Data handling questions for an AI vendor, with what a good answer sounds like
Question | What a Good Answer Sounds Like | Red Flag |
|---|---|---|
Is our data used to train or improve your models, including in de-identified, aggregated, or feedback form? | A written exclusion in the contract that covers inputs, outputs, and de-identified derivatives, with any feedback feature disabled by default at the organization level | “We do not train on customer data” with no mention of de-identified or aggregated use, or a commitment that appears only on a web page and is missing from the contract |
How long are our prompts and answers retained, and can retention be set to zero? | A stated retention period the office’s administrator controls, with a zero retention option available in writing for the products the office uses | Retention “for as long as needed to provide the service,” or a retention period the vendor can change without notice |
Where is our data processed and stored? | Named regions, with the office able to choose or restrict them, and a written list of any cross-border transfers | “Globally distributed infrastructure” with no region commitment |
Which subprocessors handle our data, and how are we told when the list changes? | A published subprocessor list and a contractual notice period before additions, with a right to object | A list that has to be requested, or a clause allowing new subprocessors without notice |
Who at your company can access our data, and under what conditions? | Access limited to named roles, for support or security purposes, logged, and disclosed to the office on request | Broad staff access for “service improvement” or “quality review” |
How is the data protected in transit and at rest? | Encryption in transit and at rest stated with the standard used, and keys managed separately from the data | “Industry standard security” with no specifics |
The first question deserves its own paragraph, because the second half of it is where a nominal commitment and a real one part ways. Many providers publish a default position of not training on business customers’ data. OpenAI’s enterprise privacy page states that it does not train on business data by default and offers zero data retention on eligible API endpoints, and Anthropic’s published data policy states that inputs and outputs from its commercial products are not used to train its models unless the customer opts in. Those are the right kind of answer, and the office should still read the next clause. Terms across the industry commonly allow feedback a user submits, or data that has been stripped of identifiers, to be used for analysis and product improvement. Wealth data that has been de-identified is still the office’s data, and a family’s portfolio is recognizable from its shape long after the family’s name is removed. The question to put in writing is whether the exclusion covers de-identified and aggregated derivatives as well as the raw data, and whether any feedback feature can be switched off for the whole organization.
A no-training commitment that excludes only identifiable data still allows the vendor to learn from the office’s data in aggregate. The question that separates a real commitment from a nominal one is whether de-identified derivatives are excluded as well.
What Access and Control Questions Should You Ask?
Access and control questions go to the software vendor that connects the AI assistant to the office’s data, because that vendor decides what the AI assistant can see and do.
Table 3. Access and control questions for the software or wealth platform vendor
Question | What a Good Answer Sounds Like | Red Flag |
|---|---|---|
Does the AI assistant inherit the connected user’s permissions, or does it get access of its own? | The AI assistant sees exactly what the user who connected it can see in the product, and nothing more | A service account with product-wide access, or “the AI assistant has read access to the workspace” |
What has to happen before the AI assistant can change, post, or delete anything? | Reading is the default; every write action requires explicit approval from a person, every time or per action type | Write access granted at connection time, or approval that can be switched off globally |
Does the product log every query the AI assistant runs against our data, and can we get the record when we need it? | Yes: every query is logged by the platform with the user, the time, and what was requested, and the office can obtain the record on request | No logging of AI queries, or a log the vendor cannot produce when the office asks |
How quickly can we switch the connection off, and who can do it? | Any administrator, immediately, from inside the product, with the AI assistant’s access ending at that moment | Revocation by support ticket, or tokens that stay valid until they expire |
How does the AI assistant authenticate, and does it use our identity provider? | Through the office’s existing single sign-on, with the same multi-factor requirements as a person | A separate credential for the AI assistant that sits outside the office’s identity controls |
For example, an AI assistant connected through Aleta’s two-way MCP layer works with the connected user’s permissions, reads within them, and acts only after explicit approval, with every query it runs against the platform logged and the connection revocable by the office at any time. Those answers are published, so a family office evaluating the platform can read them before the first call, which is the standard the second column of the table describes. The capital call workflow in our article on real AI prompts family offices run shows the approval step in practice, with the AI assistant preparing the postings from five notices and stopping for a person before anything is posted.
What Security Evidence Should an AI Vendor Provide?
Answers describe intent, and evidence shows whether the intent is tested, so six items of security evidence belong in every AI vendor file whatever kind of vendor it is.
An independent audit report, such as a SOC 2 Type II report or an ISO 27001 certificate, with the office reading the scope section to confirm that the product it is buying is the product that was audited. A penetration test summary from an outside firm, dated within the past year. A contractual incident notification timeline, stated in hours and running from the moment the vendor becomes aware of an incident, since a clock that starts after the investigation ends can run for weeks. A written answer to whether the vendor has had a reportable breach in the past three years, and what changed afterward. Cyber insurance, with the office asking for the coverage limit. A signed DPA that names the office as controller, the vendor as processor, and the AI assistant provider as subprocessor where that applies.
The audit report is the item most often misread. A report covers the systems and the period in its scope statement, and an AI feature added after the audit period or run on infrastructure outside the scope is not covered by it. The question to ask is whether the AI capability the office is evaluating sits inside the audited scope, and if the answer is no, when the next report will include it.
What Contract and Exit Terms Belong in an AI Vendor Agreement?
The contract is where the answers become enforceable, and the exit terms are the ones a family office regrets skipping.
Deletion on termination, with written confirmation and a stated period within which backups are purged. Export of the office’s data in a usable format before deletion, at no additional cost. Notice before the vendor changes the underlying model, adds a subprocessor, or revises its data terms, with the right to terminate without penalty if the office objects. Limits on price changes at renewal. Liability that is not capped at a trivial multiple of fees where the vendor’s failure exposes the office’s data. Audit rights, or at minimum the right to receive the vendor’s own audit reports on request each year. An AI assistant provider on an enterprise tier will usually have standard positions on each of these, and a software vendor connecting to that provider should be able to show how its own terms pass the same commitments through.
Do Consumer AI Tools Pass Due Diligence?
A consumer AI account fails the training, retention, and staff access questions by default, and no internal policy changes the terms attached to it.
On a consumer account the terms typically let the provider improve its models on conversations unless the user opts out, retention follows the provider’s defaults rather than the office’s, and the office has no administrator, no log, and no contract. That is the account staff reach for first, which is why the ungoverned connection is the larger risk in most family offices. The enterprise tier is the minimum for wealth data, and family offices that want prompts and answers to stay inside an environment they administer can run a model in their own cloud account.
How Does Aleta Answer AI Vendor Due Diligence Questions?
Aleta is a total wealth platform that delivers consolidated wealth reporting for family offices, built on an open, AI-native architecture. It is a software vendor in the sense of Table 1, SOC 2 Type II certified and named Best Data Provider at the Family Wealth Report Awards 2026, and its answers to the platform-side questions are published.
Table 4. Aleta's answers to the platform-side AI vendor due diligence questions
Question | Aleta's Answer |
|---|---|
Is family office data used to train AI models? | No. Client data is not used to train Aleta Intelligence, the platform’s suite of AI tools, or any public AI model, and connecting an AI assistant to the platform does not require it |
What does a connected AI assistant see? | The connected user’s own permissions, and nothing beyond them |
What happens before the AI assistant changes anything? | Anything beyond reading requires explicit approval from a person |
Is the AI assistant’s activity logged? | Every query an AI assistant runs against the platform is logged |
Can the office switch the connection off? | Yes, at any time, by the office |
What about the AI assistant provider’s side? | No platform vendor can answer for what an AI assistant provider does with an answer after delivery, and Aleta does not claim to. The office verifies that side in its own contract with the provider, using the questions in Table 2 |
The last row is the one to read twice. A platform vendor controls what leaves the platform and can commit to that in writing. What the AI assistant provider does with an answer once it arrives is governed by the office’s agreement with that provider, and a platform vendor that claims otherwise is answering a question it cannot answer.
How Should a Family Office Run AI Vendor Due Diligence?
AI vendor security due diligence runs on the process a family office already uses for custodians and administrators, with the AI vendors added to the list.
Ownership sits with whoever owns third-party risk today, usually the CFO, the controller, or the office lead, with the person who will use the tool answering the practical questions. The questions in Tables 2 and 3 go to the vendor in writing, and the answers come back in writing; a call can explain an answer, but the written version is the one that counts. Each answer is scored on two points: is it specific, and is it in the contract. A specific answer that appears only on the vendor’s website scores half, since web pages change without notice. The evidence from the security section is collected once and filed with the DPA. The whole review is repeated once a year and whenever the vendor changes its model, its subprocessors, or its terms, since each of those changes can move an answer from the good column to the red flag column without anything else looking different. Ocorian’s 2026 report puts the standing requirement in one line: managing third-party relationships well “requires more than onboarding questionnaires.”
For the process itself, the NIST AI Risk Management Framework gives family offices that want a formal structure a vendor-neutral one, organized around governing, mapping, measuring, and managing AI risk. Most family offices will not need it in full.
The test of an answer is whether it is specific and whether it is in the contract. A vendor that has done this before hands over a document.
Frequently Asked Questions About AI Vendor Due Diligence
What questions should a family office ask an AI vendor before signing a contract?
What questions should a family office ask an AI vendor before signing a contract?
Whether the office’s data is used to train or improve the vendor’s models, including in de-identified or aggregated form; how long prompts and answers are retained and whether retention can be set to zero; where the data is processed and stored; which subprocessors handle it; who at the vendor can access it; and what happens to the data when the contract ends. For a vendor that connects an AI assistant to the office’s systems, the office also asks whether the AI assistant inherits the user’s permissions, whether it needs approval before acting, whether every query is logged, and how quickly the connection can be switched off. A platform vendor such as Aleta publishes its answers to that second set; the AI assistant provider’s answers come from its enterprise contract.
What is zero data retention in an AI contract?
What is zero data retention in an AI contract?
Zero data retention is a contractual arrangement in which the AI provider does not store the family office’s prompts or the model’s answers after the response has been delivered. It is typically offered on enterprise or API tiers, consumer products do not include it, and it may apply only to specific products or endpoints, so the office should confirm in writing which of the tools it uses are covered.
Does de-identified data count as training on my family office’s data?
Does de-identified data count as training on my family office’s data?
Under many providers’ terms it does not, which is exactly why the question matters. A commitment not to train on customer data often excludes only identifiable data and leaves room for de-identified, aggregated, or feedback-derived data to be used for analysis or model improvement. A family’s portfolio is recognizable from its shape after the name is removed, so the office should ask for an exclusion that covers de-identified derivatives as well and confirm that any feedback feature can be disabled for the whole organization.
Is a SOC 2 Type II report enough to approve an AI vendor?
Is a SOC 2 Type II report enough to approve an AI vendor?
A SOC 2 Type II report shows that the controls in its scope operated over the audit period. It does not cover an AI feature added after that period, infrastructure outside the scope statement, or the vendor’s contractual terms on training and retention. The report is one of six pieces of evidence, and the family office reads its scope section before relying on it.
Do I need a data processing agreement with an AI assistant provider?
Do I need a data processing agreement with an AI assistant provider?
Yes, where the family office’s data includes personal data, which wealth records almost always do. The AI assistant provider processes that data the moment an answer reaches it, so it is a processor under GDPR and a service provider under US state privacy laws such as California’s, and a DPA is the document that sets the terms. Enterprise tiers of the major AI assistants include a DPA as standard; consumer tiers do not.
How often should a family office repeat AI vendor due diligence?
How often should a family office repeat AI vendor due diligence?
At least once a year, and again whenever the vendor changes its underlying model, adds or replaces a subprocessor, or revises its data terms. Each of those changes can alter a training, retention, or access answer without any visible change in the product, so the review is tied to vendor changes as well as to the calendar.
How does Aleta answer AI vendor security due diligence questions?
How does Aleta answer AI vendor security due diligence questions?
Aleta publishes its platform-side answers. Client data is not used to train AI models, an AI assistant connected to the platform sees only what the connected user can see, anything beyond reading requires explicit approval, every query the AI assistant runs against the platform is logged, and the family office can revoke the connection at any time. No platform vendor can answer for what an AI assistant provider does with an answer after delivery, so the office verifies that side in its own contract with the provider.
You might like these reads
Is It Safe to Connect an AI Assistant to Family Office Data in 2026?
Aleta on what to check on training, retention, permissions, and logs before you connect.
Sep 28, 2026
AI,
Family offices
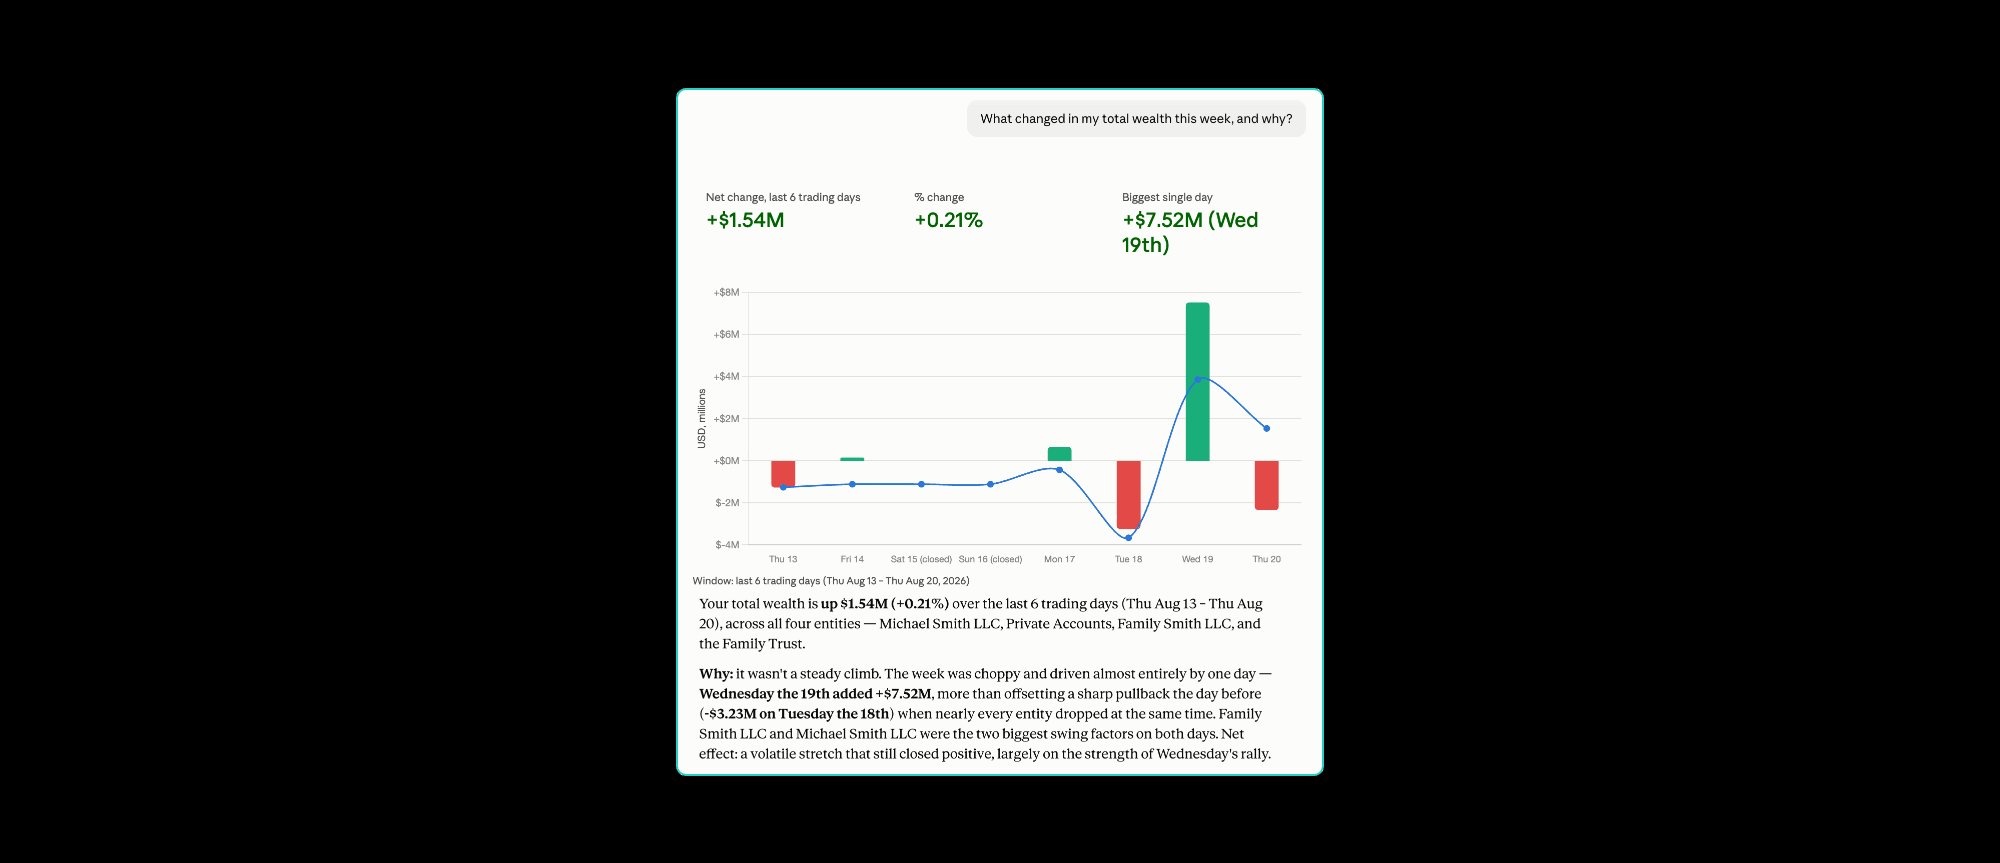
Real Prompts You Can Steal: How Family Offices Use AI Agents on Their Wealth Data
11 real prompts family offices run with AI agents on wealth data, from performance and liquidity to compliance and automation, with answers and screenshots.
Aug 25, 2026
AI,
Family offices
MCP: What It Is and Why It Matters for Family Offices
What is MCP in family office software? A plain-language guide to the Model Context Protocol, how it differs from an API, and what to check on security.
Aug 24, 2026
AI,
Family offices